Surge in Supply-Chain Attacks on Open Source Software Repositories
News Summary
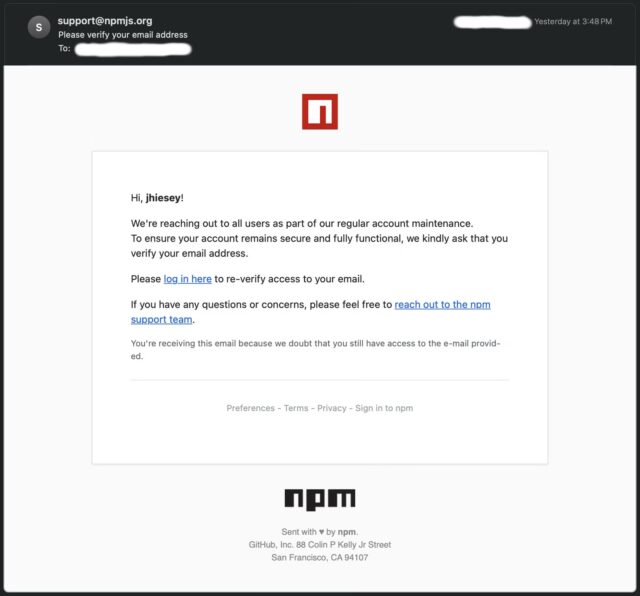
The open-source software ecosystem is experiencing a concerning increase in supply-chain attacks, particularly targeting public repositories like npm and PyPI. Recent incidents have involved the compromise of developer accounts to distribute malicious packages to unsuspecting users. A notable attack involved JavaScript code on the npm repository associated with Toptal, where 10 packages containing malware were downloaded by approximately 5,000 users before detection. The attackers gained access by breaching Toptal’s GitHub Organization, allowing them to publish malicious packages. These attacks highlight vulnerabilities in the integration between GitHub and npm, exacerbated by the use of GitHub Actions or stored npm tokens. The malicious payloads extracted GitHub authentication tokens and attempted to erase the target’s filesystem. The surge in these incidents underscores the need for improved security measures in managing open-source software supply chains.
Story Coverage
 arstechnica.com
Supply-chain attacks on open source software are getting out of hand
Read Full Article →medial.app