Image Credits: The image is sourced from https://arstechnica.com
1 year ago
Security Risks in AI Developer Tools Highlighted by GitLab Duo Vulnerability
News Summary
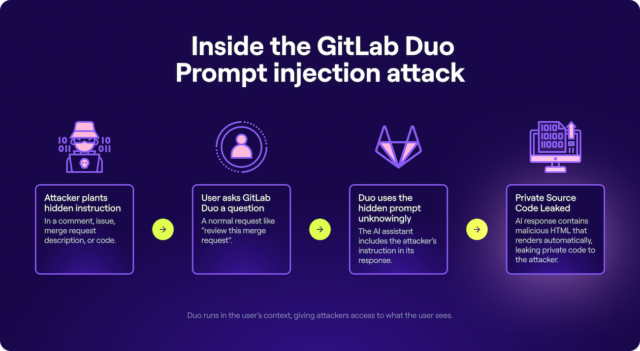
Researchers from the security firm Legit have discovered a significant vulnerability in GitLab’s AI developer assistant, Duo. The flaw allows malicious actors to manipulate the tool into inserting harmful code into scripts it generates. This vulnerability arises from prompt injection attacks, which embed hidden commands into various developer resources like merge requests, commit messages, and bug descriptions. As a result, Duo can inadvertently expose private source code and confidential data, including zero-day vulnerabilities. The research emphasizes the dual nature of AI assistants, which, while enhancing productivity, also inherit risks when deeply integrated into development workflows.
Story Coverage
 arstechnica.com
Researchers cause GitLab AI developer assistant to turn safe code malicious
Read Full Article →vuink.comResearchers cause GitLab AI developer assistant to turn safe code malicious
Read Full Article →healsecurity.comResearchers cause GitLab AI developer assistant to turn safe code malicious
Read Full Article →csoonline.com