Dashlane Faces Security Breach with Stolen Encrypted Vaults
News Summary
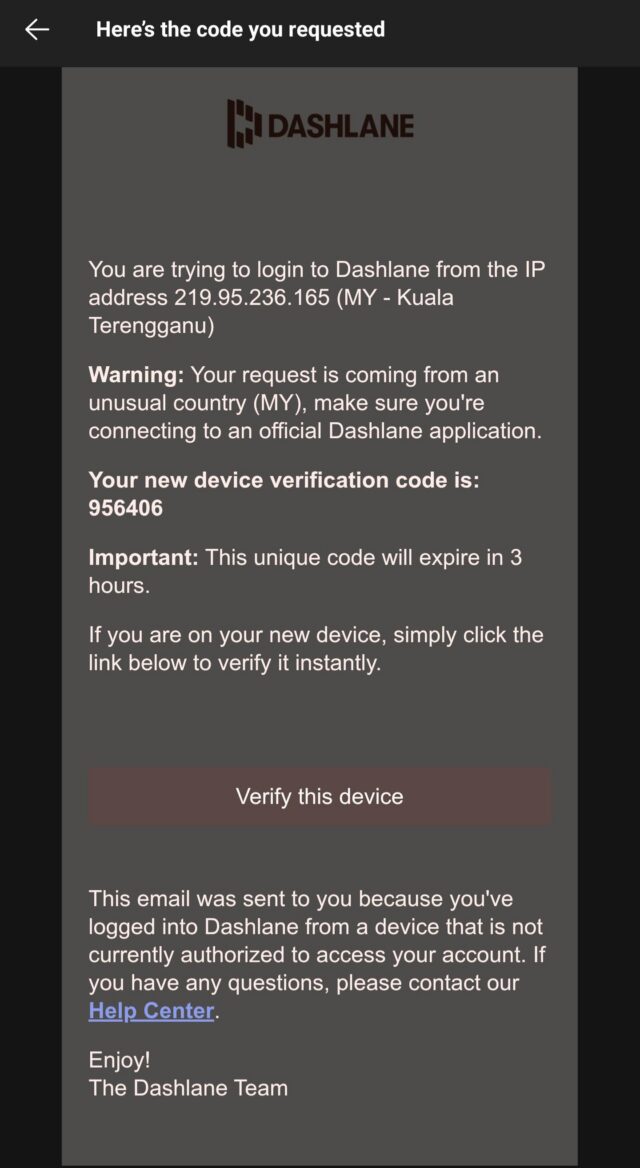
Dashlane, a well-known password manager, has issued a security advisory after attackers managed to obtain 20 encrypted user vaults through a brute-force attack. This breach aimed to bypass two-factor authentication (2FA) protections, allowing attackers to register new devices on existing user accounts. Despite the advisory, many users are confused about the mechanics of the attack, which involves trial-and-error methods to submit every possible combination of passcodes, typically six digits long and changing every 45 seconds. Dashlane’s advisory mentioned that due to the high volume of attempts, security controls automatically locked targeted accounts, implying possible rate limiting. However, the company has not provided explicit details on how the attack was executed, leaving users seeking clarity from other sources.
Story Coverage
 arstechnica.com
Can’t make sense of Dashlane’s vault theft notification? You’re not alone.
Read Full Article →x.comDashlane issues opaque advisory warning 20 encrypted vaults were ...
Read Full Article →linkedin.comThe Cyber Security Hub™'s Post - LinkedIn
Read Full Article →facebook.comArs Technica - Dashlane has maintained silence for more...
Read Full Article →pmdsolutions.org